
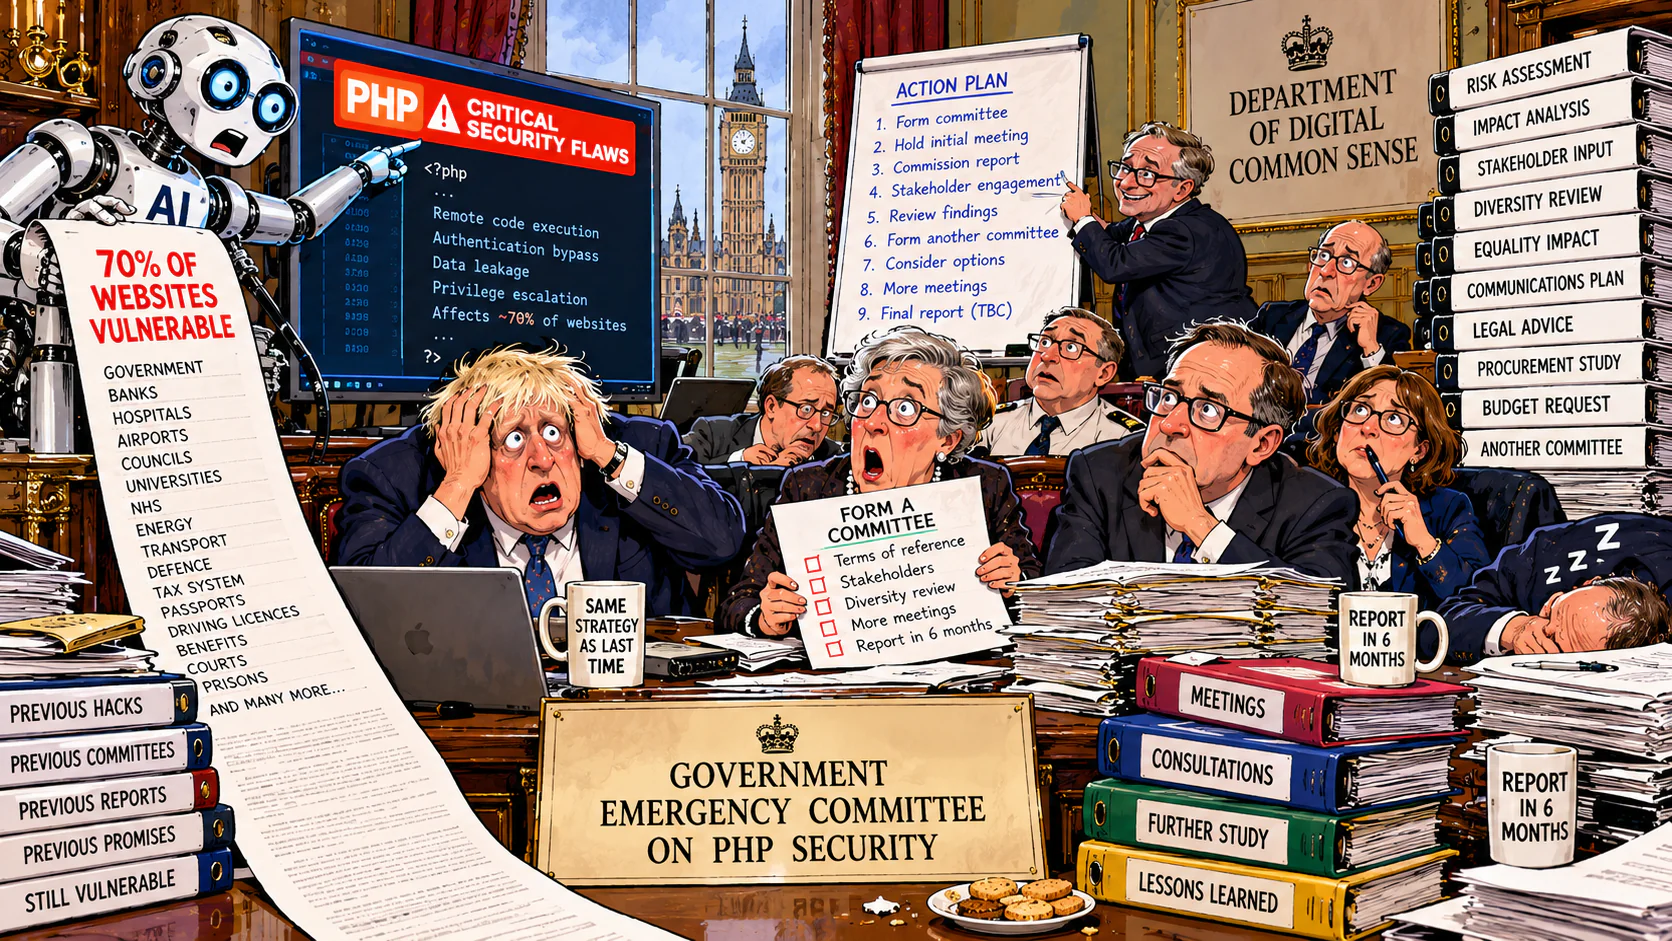
Machine Offers to Fix Everything Today, Chairman Declines
LONDON, October 22, 2026 – Artificial intelligence has caused considerable embarrassment among the world’s technology administrators after helping cybersecurity researchers expose serious vulnerabilities in software used across much of the internet, apparently without first establishing a steering committee, appointing a chairperson or commissioning a report from an expensive management consultancy.
According to the Associated Press investigation into AI-assisted PHP vulnerability research, AI helped researchers determine how previously identified weaknesses in PHP could be exploited and assisted in validating solutions.
The discovery threatened to revolutionize modern administration by demonstrating that identifying a problem and working toward a solution do not necessarily require eleven meetings and a stack of PowerPoint presentations.
Technology managers reacted with alarm.
“We cannot have machines solving problems before management has had an opportunity to discuss them,” said an international technology administrator. “If this becomes standard practice, what exactly will senior management do all day?”
Committee Formed to Investigate Whether a Committee Is Necessary
The first response was to establish the International Committee on Artificial Intelligence Findings, Digital Resilience and Appropriate Committee Procedures. Its opening meeting lasted four hours. The first hour concerned the committee’s name. The second concerned whether participants should be called members, stakeholders or strategic solution partners. The third examined the environmental consequences of printing the agenda. The fourth was devoted to scheduling the next meeting, which was eventually postponed because several participants had another meeting about meetings.
Artificial intelligence, meanwhile, had identified additional technical issues and helped researchers test possible safeguards. A computer submitted a brief suggestion that vulnerable systems should be patched promptly.
Committee members expressed concern about the computer’s confrontational tone. One delegate demanded that the word “promptly” be replaced with “following an appropriately inclusive consultation process.” Another argued that the computer’s use of direct language reflected an unacceptable preference for results over procedure.
PHP Foundation Admits Delays on Known Security Flaws
The PHP Foundation acknowledged that the vulnerabilities had been known since at least 2024 and that competing technical approaches, limited resources and decision-making failures contributed to the delays.
For technology administrators, this was the most reassuring part of the entire crisis. At last, someone in the software industry was behaving like a conventional institution.
The official PHP security releases issued on October 21 addressed two critical vulnerabilities, with updated versions made available for affected systems. The flaws were rated 9.2 on the CVSS 4.0 severity scale, a figure normally associated with serious technical emergencies.
Government administrators immediately proposed a more familiar rating system. Under the proposed Public Sector Urgency Index, an event rated 9.2 would require an initial committee meeting within six months, subject to staff availability. Anything above 9.5 would trigger an urgent email marked “For Information Only.” A perfect score of 10 would allow managers to consider bringing forward the date of the next review.
AI Threatens the Management Consultancy Business
The crisis also created anxiety among the international consultancy industry. For years, consultants have earned substantial fees explaining that organizations need to become more efficient, particularly after hiring consultants has made them less efficient. Artificial intelligence now threatens this carefully balanced ecosystem.
A consultancy executive warned that computers might eventually identify obvious problems without charging organizations £4 million for a transformation roadmap.
“Suppose a company has an outdated computer system,” he said. “A machine might simply recommend updating it. Where does that leave our twenty-eight-page executive summary?”
The consultant proposed an immediate inquiry into whether artificial intelligence should be required to employ consultants before producing recommendations. The inquiry concluded that consultants were essential, although its methodology consisted mainly of interviewing consultants.
Can AI Fix Software Vulnerabilities Faster Than a Committee?
Researchers have stressed that fixing complicated software vulnerabilities is not as simple as identifying them. Patches need developing, testing and deployment across different systems. Even so, AI has clearly changed the speed at which technical problems can be investigated, which leaves a difficult future for institutions built around the principle that every solution must first be converted into an administrative problem.
A computer was invited to explain its methods at a technology conference.
“I examined the available evidence, identified the weakness and evaluated possible fixes,” it answered.
The audience remained silent.
“Could you explain that in a 140-slide presentation?” asked the chairman.
“No,” replied the computer. “That would be inefficient.”
The chairman immediately suspended proceedings.
Emergency Summit Ends With Certificates and No Patches
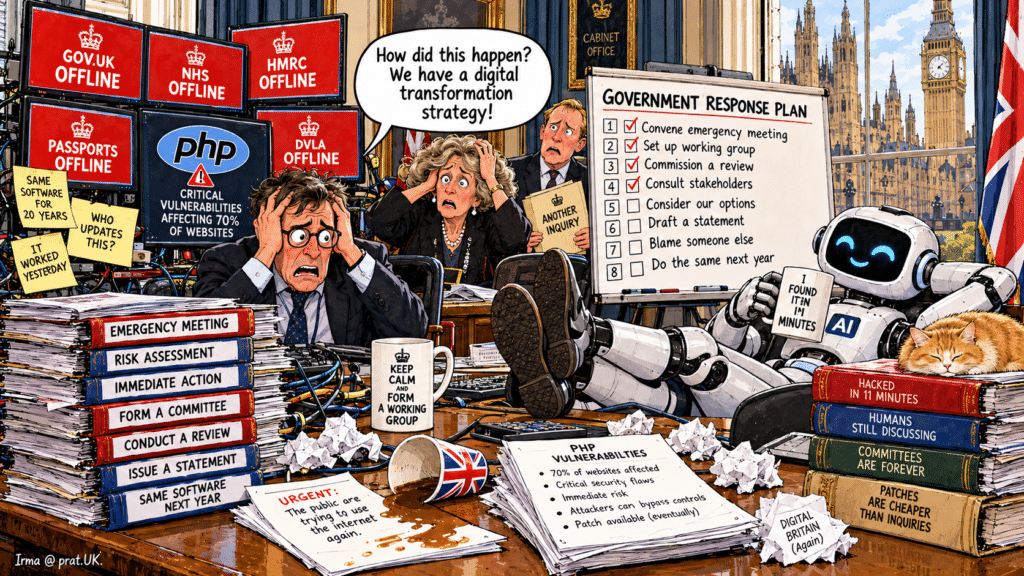
By the conclusion of the summit, representatives had approved a landmark international agreement. The agreement committed participating institutions to establish a committee tasked with developing recommendations for the formation of a future working group to study artificial intelligence’s capacity for making committees unnecessary.
No security vulnerabilities were repaired during the meeting. Organizers declared the conference an overwhelming success anyway. Every attendee received a certificate, consultants received their fees and the final report recommended further research.
Artificial intelligence responded by asking whether anyone would like it to fix something.
The chairman said the question had been added to the agenda for next Thursday.
The machine then committed its most controversial act yet. It asked why they couldn’t simply do it today.
The PHP Foundation’s acknowledgment of delays, AI’s role in demonstrating exploitability and the October 21 patches are all on the public record through the Associated Press and PHP.net.
Humorous Observations on the AI Security Summit
- AI finds the security problems, and what do the government committees do? They launch an investigation into whether the AI should be allowed to embarrass human intelligence. It’s not embarrassing us. We’re doing that. The AI’s just standing there.
- The PHP Foundation admitted its decision-making process had problems, and the government officials loved it. Finally, somebody who can maintain a bureaucratic delay without a penny of government money. That’s the private sector for you. Efficient at being slow.
- A computer can find a vulnerability in a few hours. Humans need three weeks to figure out which department gets the email. It’s an email. It doesn’t have a department.
- AI can find security holes, help check the fixes, and wade through code nobody’s read since the Obama administration. What it cannot do is get a senior manager to cancel a Thursday afternoon meeting. That’s the final boss.
- The scary part isn’t that computers have vulnerabilities. Computers always have vulnerabilities. The scary part is that the AI found years of human procrastination in an afternoon and never once asked for overtime.
An AI offered to write this disclaimer in four seconds; a committee is still reviewing the offer. The PHP emergency is real, while the summit, the chairman and the certificates are comic, and the 70 per cent figure reflects how widely PHP is used rather than proof of compromise. Overseen by the world’s oldest tenured professor and a philosophy major turned dairy farmer, who hold no CVSS rating. See how to tell satire from real news.

Carys Evans is a prolific satirical journalist and comedy writer with a strong track record of published work. Her humour is analytical, socially aware, and shaped by both academic insight and London’s vibrant creative networks. Carys often tackles media narratives, cultural trends, and institutional quirks with sharp wit and structured argument.
Her authority is reinforced through volume, consistency, and reader engagement, while her expertise lies in combining research with accessible humour. Trustworthiness is demonstrated by clear labelling of satire and an ethical approach that values accuracy and context.
Carys’s work supports EEAT compliance by offering informed satire that entertains while respecting readers’ trust.


